


Fusion Tech Multi-Services delivers end-to-end, compliance-driven cybersecurity auditing services that balance strategic governance with technical depth. Our audit engagements are aligned to global regulatory and industry standards such as ISO/IEC 27001, NIST Cybersecurity Framework, PCI DSS, HIPAA, and GDPR, enabling organisations to demonstrate due diligence, achieve continuous compliance, and strengthen their Information Security Management Systems (ISMS). On the technical front, we deploy certified auditors and security practitioners to conduct exhaustive assessments, including Vulnerability Assessment and Penetration Testing (VAPT), Secure Configuration & Patch Compliance Reviews, Secure Code Audits, Cloud Security Posture Management (CSPM), SIEM-driven Log Analysis, and Red Team/Blue Team Exercises. Using advanced techniques such as threat modelling, risk quantification, and zero-trust validation, we uncover misconfigurations, unpatched systems, and exploitable attack vectors across hybrid infrastructures encompassing networks, endpoints, cloud workloads, and OT/IoT devices. Findings are translated into prioritised risk matrices, remediation roadmaps, and governance gap reports, empowering leadership teams to make informed security investments while enabling technical teams to harden defences against Advanced Persistent Threats (APTs), insider threats, and evolving attack surfaces. By combining regulatory alignment with technical precision, Fusion Tech Multi-Services helps organisations reduce cyber risk, enhance operational resilience, and build stakeholder trust in a hostile threat landscape.
Why choose Fusion Tech Multi-Services
Certified leadership: The company’s top management hold industry-leading certifications including CISA and CISM, and are broadly Cyber Security Certification qualified — ensuring governance-first thinking and technical rigor across every engagement.
Depth + practicality: We balance deep technical testing with business context so findings are actionable and prioritised according to real organisational risk.
Regulatory & standards alignment: Experienced in ISO/IEC 27001, NIST CSF, PCI DSS, GDPR and other sector regulations — we align audits to the controls that matter to you.
Transparent, repeatable methodology: A phased, transparent approach (scoping → testing → reporting → remediation → re-test) ensures predictable outcomes and measurable improvements.
Local presence, global standards: While rooted in India, our team follows international best practices and can work with distributed environments and multi-cloud architectures.
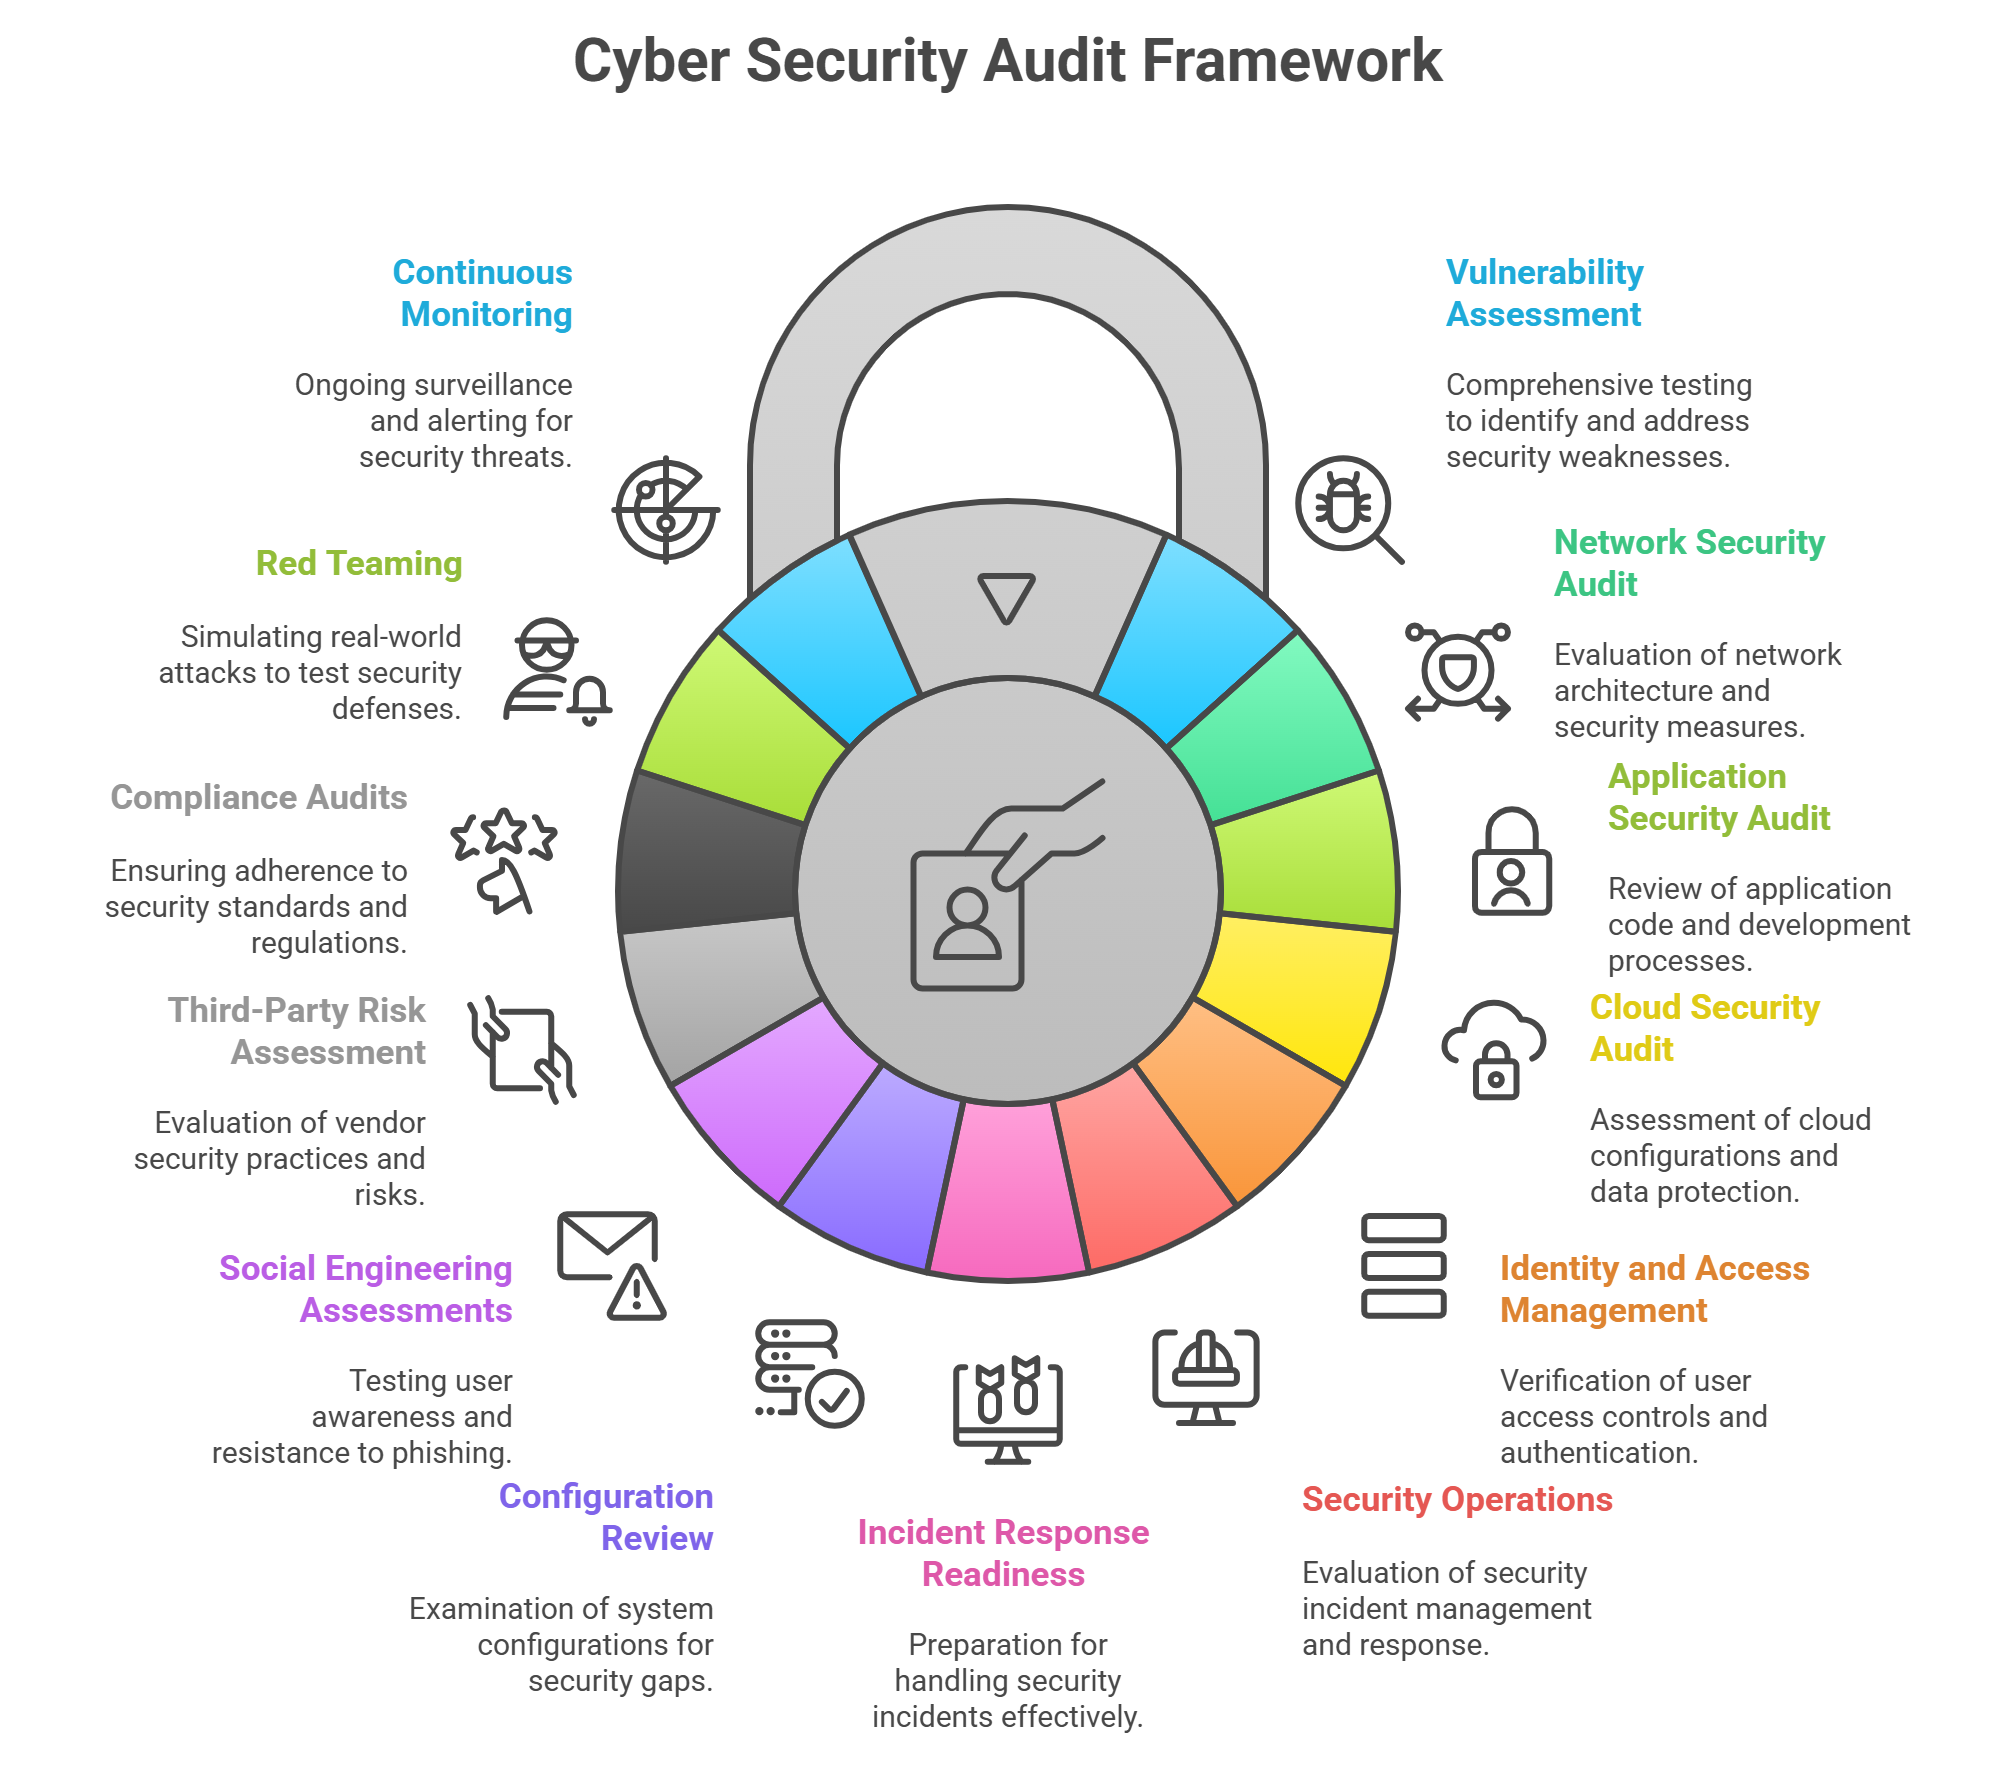
Our audit methodology (what you can expect)
Engagement kickoff & scoping — define goals, assets, timelines and rules-of-engagement.
Information gathering — asset discovery, architecture review and stakeholder interviews.
Threat modelling & test planning — tailor test scenarios to likely threats and business-critical assets.
Technical testing & validation — combination of automated scanning and manual testing by certified pentesters.
Analysis & risk prioritisation — each finding is rated for severity, exploitability and business impact.
Reporting & remediation roadmap — clear executive summary, technical details, and prioritized fixes with suggested timelines and owners.
Remediation support & re-test — guidance during remediation and validation once fixes are applied.
Continuous improvement — option for periodic audits, monitoring or managed services to keep risk reduced.
Deliverables
Executive Summary — one-page view for leadership with risk posture and recommended next steps.
Detailed Technical Report — reproducible steps, evidence, risk ratings, and remediation guidance.
Remediation Roadmap — prioritized fixes mapped to business impact and estimated effort.
Compliance Mapping — control-level mapping to frameworks requested by client (eg. ISO27001 / PCI DSS).
Re-test Evidence — verification that critical issues were remediated.
Optional: SIEM Rules & Detection Playbooks — actionable detections and suggested playbooks to improve SOC capability.
Tools, techniques and qualifications
We use a mix of industry-standard commercial scanners and in-house manual testing techniques to avoid false positives and surface real risks.
Our engineers and auditors are certified (CISA, CISM, OSCP, CEH, CISSP and others) — and our leadership is specifically CISA & CISM qualified, ensuring audit governance and program-level expertise.
SLAs & timelines
Typical small-to-medium VA/PT: 2–4 weeks from kickoff to report.
Full enterprise audits or red-team engagements: timelines vary (4–12+ weeks) depending on scope.
Re-tests: usually completed within 5–10 business days depending on the number of validated fixes.
(We will provide exact timelines in the engagement proposal.)
Frequently asked questions (FAQs)
Q: Will the audit disrupt my operations? A: We plan tests to minimise disruption — production-impacting tests are performed in agreed windows, with rollback plans in place.
Q: Are findings confidential? A: Absolutely. All audit findings, evidence and reports are treated as confidential and can be governed by an NDA.
Q: Do you help with remediation? A: Yes — we provide remediation guidance, patch prioritisation and re-testing. We can also provide hands-on remediation as a separate service.
Q: Can you help prepare for ISO27001 or PCI audits? A: Yes — we perform pre-certification gap analyses and help implement controls required for certification.

